I have been testing the new Cisco ISR 1113 Router from Cisco, and done a bit of a video overview. Perfect for offices and it can handle your 1Gig WAN Ethernet/SFP/VDSL/GFAST link, LTE, or even BGP,MPLS, etc and has various licensing on offer. It is also SD-WAN Ready.
Category: Cisco
I wanted to try do something on my Cisco ASA to setup incoming IKEV/IPsec/L2TP VPN to allow access to the local LAN and also the internet connection which the ASA Uses. So when a client connects to the VPN, they can access the local lan, as well as the internet connection that sits off from the ASA.
In order to set this up, we have to have something like this going, all performed in enable configuration mode.
- Define your VPN Pool of addresses eg
ip local pool VPNUsers 192.168.20.1-192.168.20.30 mask 255.255.255.224 - Relax the security rules between the interfaces a bit
same-security-traffic permit intra-interface - Create an object for example like VPN, then NAT the outside interface to the outside, this allows routing of internet from VPN to the ASA using the ASA’s ISP connection on outside
object network VPN
   subnet 192.168.20.0 255.255.255.224
   nat (outside,outside) dynamic interface
- Allow VPN Interface “Hairpin” on same interface and access to local LAN/Internet resources
nat (outside,inside) source static VPN VPN - Create a VPN Clients Out ACL, to allow the VPN Client subnet, access from its subnet to any IP address on the outside (in our case the local LANs or internet)
access-list VPN_CLIENTS_OUT extended permit ip object VPN any - Modify the group policy tunnel attributes attached to your tunnel. In my scenario below VPN Clients will use the Cloudflare DNS, utilise the correct ACL for access, allowed IKEV or L2TP protocols, all traffic will be tunneled and no split traffic permitted on client, and the IP address pool will be utilised from our VPNUsers pool
group-policy yourtunnel attributes
  dns-server value 1.1.1.1
  vpn-filter value VPN_CLIENTS_OUT
  vpn-tunnel-protocol ikev1 l2tp-ipsec
  split-tunnel-policy tunnelall
  address-pools value VPNUsers
- Once the above is implemented, the VPN clients will have access to the Local LAN, and to the Internet connected to the ASA. The above configuration does not take into consideration the complete VPN Tunnel setup, this additional configuration assumes you already have an existing complete tunnel setup.
This took me some time to get working, so I wanted to put some of my research on my blog incase anyone wishes to do the same, feedback welcome 🙂
I recently have purchased 2 x Cisco 3802 , and 2 x Cisco 1852 Access points to work with the Cisco 2504 WLC Controller. I really wanted to upgrade to AC wifi and take advantage of all that Cisco have to offer in the wireless world and put it through some tests and performance. Initially i found it great on Windows Laptops and Macbooks, however i had major issues with Apple IOS 11 and Apple TV. Connections would constantly drop and would not work as well. I was testing on the 5Ghz/80Mhz band, and i seriously thought there was an issue with this band, as switching things to 2.4Ghz/20Mhz seemed to work better.
I raised a Cisco TAC case to further investigate these issues and we found that:
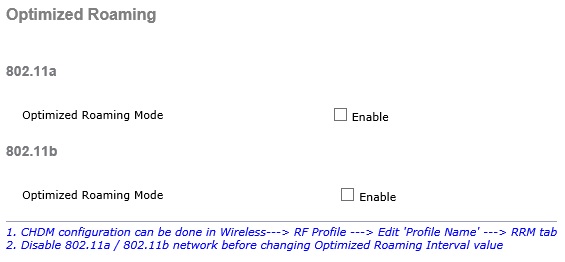
1) Optimized Roaming was enabled for 802.11a and 802.11b. (On WLC: Wireless > Advanced > Optimized Roaming)
This caused many issues with the Apple TV and Iphones/Ipads, and disabling this fixed the Apple TV, but not fully the Iphones and Ipads.
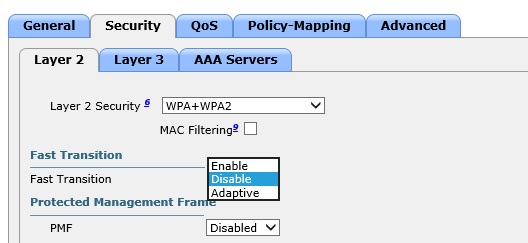
2) Fast Transition was enabled with Adaptive (On WLC: WLANS > “Your SSID” ID > Security > Layer 2 > Fast Transition)
Having Fast Transition enabled caused the significant issues with Iphones and Ipads with wireless connectivity and dropping. Once this was switched off we immediately noticed the performance improvement and roaming.
Cisco advised that the IOS 11 is buggy when it comes to the implementation of Fast Transition as we went through many debugs. They advised I needed a Apple Enterprise Support contract for Apple to just look at it, which I couldnt afford, so I have left Fast Transition “off”. The enterprise contract is like $5995 USD, or $799 USD per incident, just a bit pricy!
I also asked if there was any benefits to Fast Transition being “on”, and they advised it was only beneficial if my wireless setup is 802.1X and this improves the roaming between AP’s and going through Radius etc. My scenario only had WPA2 Pre-Shared key, so i could leave the Fast Transition set to Off without any issues.
Cisco Apple best practice document found here, advises FT should be set to Adaptive and left on, however as we found IOS 11 has severe issues with their implementation of FT..
I queried Cisco whats going on here.. and why there is so many issues and differentiates from their document and their advise was:
FT will always be suggested on Apple enterprise environment. This can’t be removed from the document simply because new iOS on some devices are having buggy issues with it. This is something that need to be fixed on Apple side and Cisco has nothing to change on the code or document since we are following the IEEE standard that we expect Apple to also follow on their entire product line.
Unfortunately as shared before to engage Apple care , you need to have an “enterprise AppleCare support agreement” contract.
TAC can’t do anything from Cisco side for this case to move further unfortunately.
So for all of you reading and have Cisco Wireless setup, running IOS 11, and are noticing problems with Apple TV/Iphones/Ipads be warned what options are set on the WLC, and how it could affect the wireless experience.
For Apple reading, please look at your FT implementation with Cisco on IOS11, so its less buggy, especially on the 5Ghz bands.
Again, thanks for reading and any feedback welcome.
4 Comments
The next successor to the Cisco 877 I believe is the Cisco 897VA model. This model takes in Ethernet WAN/ADSL/VDSL/SFP Fibre connections. It also has 8 x 1gb user port connections, and 4 ports are PoE capable.
It allows you to do a lot with the connectivity you require, especially when it comes to the Australian NBN multi-technology mix. It will allow you to terminate your FTTP (Ethernet WAN port) and FTTN (VDSL2 port).
One thing I like about this router is the casing is not plastic like the Cisco 877 and it is metal instead, and it has a nice look and feel to it
Here are some photos of this model:


If you are looking for the latest software for this one to work on the NBN as well see Cisco 897 Menu in the blog above.
Hopefully this has given you a better insight of the new Cisco 897VA Model, and some nice software to operate it on the NBN or your own specific network.
As always welcome any feedback how this router performs for you 🙂
16 CommentsOn the 24 August 2016 Cisco released new ASA code 9.6.2 adding further support to the IPv6 protocol – Prefix Delegation. Recently Telstra (Australian ISP) has enabled IPv6 on NBN (National Broadband Network) services and I thought what better way to try out this than on my ASA 5506-X. I will go through the basic process on getting IPv6 to work on a Cisco ASA with PD.
In the steps below GigabitEthernet1/1 is the outside interface, and GigabitEthernet1/2 is the inside interface.
1)The first step is configuring IPV6 on the outside interface. At this point, no IPV6 address will be configured in the firewall.
interface GigabitEthernet1/1
 ipv6 address autoconfig default trust dhcp
 ipv6 address dhcp default
 ipv6 enable
 ipv6 nd managed-config-flag
 ipv6 nd other-config-flag
 ipv6 dhcp client pd ciscoasa
2) The ISP will provide the prefix which has to be used, and some data has to be collected by using the following commands:
show ipv6 dhcp interface outside
With this, you will have the info about the default-dateway (Reachable via address) and the subnet assigned by the ISP (Prefix)
GigabitEthernet1/1 is in client mode
 Prefix State is OPEN
 Renew will be sent in 01:37:04
 Address State is SOLICIT
 List of known servers:
 Reachable via address: fe80::fac0:1ff:fe70:17c0
 DUID: 000100011914BB0A00144FFA6B62
 Preference: 0
 Configuration parameters:
 IA PD: IA ID 0x00020001, T1 7200, T2 11520
 Prefix: 2001:8003:a02c:8700::/56
 preferred lifetime 14400, valid lifetime 14400
 expires at Sep 01 2016 03:40 AM (13024 seconds)
 Information refresh time: 0
 Vendor-specific Information options:
 Enterprise-ID: 1088
 Prefix name: ciscoasa
3)Then, we need to configure the interfaces with these IP address. So, with the command show ipv6 interface, we can find the IPV6 link local for the outside interface, and configure the IPV6 address using its eui-64 portion
outside is up, line protocol is up
   IPv6 is enabled, link-local address is fe80::5287:89ff:fefc:7106
With these 2 pieces of information, we can configure the IP address to be used in the outside interface and also configure the ipv6 dhcp client pd hint. This command is necessary to ask the ISP to always provide the same IPV6 prefix so that we will keep it as if it were a static assignment.
interface GigabitEthernet1/1
 ipv6 address ciscoasa ::5287:89ff:fefc:7106/64
 ipv6 dhcp client pd hint 2001:8003:a02c:8700::/56

Note: On Telstra residential services I discovered they do not interpret the PD HINT and keep the subnet, so I have left out this line as of March 2017.
In this case, the outside network will have the following subnet 2001:8003:a02c:8700::/64
We can also configure the IPV6 default gateway with the IPV6 link- local address provided by Telstra router
show ipv6 routers
 ! Will show the link-local address to be used as the default gateway)
 Router fe80::fac0:1ff:fe70:17c0 on outside, last update 9 min
   Hops 64, Lifetime 1800 sec, AddrFlag=1, OtherFlag=0
   Reachable time 0 msec, Retransmit time 0 msec

ipv6 route outside ::/0 fe80::fac0:1ff:fe70:17c0
4) Next step is configuring the inside interface. We defined the subnet to be used so that it would not overlap the outside interface 2001:8003:a02c:8701::/64
interface GigabitEthernet1/2
 ipv6 enable
 ipv6 address 2001:8003:a02c:8701::/64 eui-64
 ipv6 nd managed-config-flag
 ipv6 nd other-config-flag

Note: On Telstra residential services the Ipv6 /64 Address will not be static. We will have to change to the following for dynamic assignments:

ipv6 address ciscoasa ::1:0:0:0:1/64

The “::1:0:0:0:1/64“  is basically the host portion of the IP address. The “ciscoasa” in this case contains the IPv6 prefix and when the ASA configures the IP address it will use the prefix and include the host portion as well and then create the IP address.
This way when the ASA reboots or looses power a new address will be ready to use if the ISP gives out dynamic /56's.
Also, a IPV6 DHCP scope was configured. In this case, it works as a stateless DHCP, as the interface will only provide the subnet used in the router advertisements and each host will include its eui-64 information to complete. In the case below I have also added in the Telstra IPv6 DNS servers however you can add your own in, or you can use import dns-server to automatically try get a server.
ipv6 dhcp pool ALCATRONV6
dns-server 2001:8000:101::1
dns-server 2001:8000:101::2
domain-name alcatron.net

interface GigabitEthernet1/2
 ipv6 dhcp server ALCATRONV6
5) Finally we can verify that the hosts are being able to get IPV6 subnet and configure their own IPV6 addresses
ciscoasa-5506X# sh ipv6 neighbor | inc 2001

2001:8003:a02c:8701:497f:8a80:b975:d580    30 a4b8.058e.8236  STALE inside
 2001:8003:a02c:8701:d565:2f36:d9b:32a7     39 1c5c.f2b4.6cad  STALE inside
 2001:8003:a02c:8701:7c57:4bd5:bb68:1b9     17 a4b8.058e.8236  STALE inside
 2001:8003:a02c:8701:c122:30ca:7b52:42ea     9 1c5c.f2b4.6cad  STALE inside
 2001:8003:a02c:8701:5f:860c:b32b:c7        43 0015.5d01.0602  STALE inside
 2001:8003:a02c:8701:597e:471f:bfd9:df3f     0 0cc4.7a70.a0a7  REACH inside
 2001:8003:a02c:8701:6820:c272:e85e:2feb    20 7081.eb1a.c6e5  STALE inside
 2001:8003:a02c:8701:f4d4:b595:88f8:374d    40 1c5c.f2b4.6cad  STALE inside
 2001:8003:a02c:8701:8574:1c6f:5fd6:1f1b    43 20c9.d07a.5777  STALE inside
And verify the IPV6 connections
ciscoasa-5506X# show conn | inc 2001

TCP outside  2404:6800:4006:806::2003:80 inside  2001:8003:a02c:8701:c122:30ca:7b52:42ea:51324, idle 0:00:32, bytes 15286, flags UIO
 TCP outside  2404:6800:4006:806::2005:443 inside  2001:8003:a02c:8701:c122:30ca:7b52:42ea:51333, idle 0:00:14, bytes 630639, flags UIO
 TCP outside  2a03:2880:f019:1:face:b00c:0:1:443 inside  2001:8003:a02c:8701:c122:30ca:7b52:42ea:51194, idle 0:02:03, bytes 17643, flags UIO
 TCP outside  2a03:2880:f019:1:face:b00c:0:1:443 inside  2001:8003:a02c:8701:c122:30ca:7b52:42ea:51193, idle 0:01:23, bytes 8865, flags UFRIO
Other useful commands you will need:
sh ipv6 interface
 ! show the configured IPV6 addresses and subnet masks
 outside is up, line protocol is up
   IPv6 is enabled, link-local address is fe80::5287:89ff:fefc:7106
   Global unicast address(es):
     2001:8003:a02c:8700:5287:89ff:fefc:7106, subnet is 2001:8003:a02c:8700::/64
   Joined group address(es):
     ff02::1:fffc:7106
     ff02::2
     ff02::1
sh ipv6 general-prefix
 ! Will show your prefix acquired via PD lifetime
 IPv6 Prefix ciscoasa, acquired via DHCP PD
   2001:8003:a02c:8700::/56 Valid lifetime 11664, preferred lifetime 11664
    Consumer List                Usage count
     outside (Address command)   1
Another issue I had is trying to get traceroute working correctly so to make sure this was working correctly i had to ensure I had the following lines. This allows ping, and echo reply to all your inside IPv6 hosts, you can tweak this however if you like with the access lists.
access-list Outside_access_in extended permit icmp6 any6 any6 echo-reply
access-list Outside_access_in extended permit icmp6 any6 any6 time-exceeded
access-list Outside_access_in extended permit icmp6 any6 any6 unreachable
access-list Outside_access_in extended permit icmp6 any6 any6
The policy maps were modified to ensure that traceroute v4 and v6 worked. You might have others in the policy-map, just leave those and append the ones below that are missing.
policy-map global_policy
 class inspection_default
   inspect icmp
   inspect icmp error
 class class-default
   set connection decrement-ttl

service-policy global_policy global
This was a steep learning experience, but finally I have dual stack IPv4 and IPv6 running on Telstra NBN through a Cisco ASA 5506-X. I have seen no articles which deal with PD delegation on Cisco ASA’s , so I thought i would do this write up so that it can benefit others. Any questions, comments, feedback, welcome as usual 🙂
5 CommentsOn the 24th of August 2016 Cisco released version 9.6.2 of its ASA software. The new version brings in more IPv6 support for the platform.
The ASA now supports the following features for IPv6 addressing:
- DHCPv6 Address client—The ASA obtains an IPv6 global address and optional default route from the DHCPv6 server.
- DHCPv6 Prefix Delegation client—The ASA obtains delegated prefix(es) from a DHCPv6 server. The ASA can then use these prefixes to configure other ASA interface addresess so that StateLess Address Auto Configuration (SLAAC) clients can autoconfigure IPv6 addresses on the same network.
- BGP router advertisement for delegated prefixes
- DHCPv6 stateless server—The ASA provides other information such as the domain name to SLAAC clients when they send Information Request (IR) packets to the ASA. The ASA only accepts IR packets, and does not assign addresses to the clients.
If you have loaded the new software how did you go in getting IPv6 working in your environment ?
At the moment I am trialing the new software on my carrier, to see whether I can get the full IPv4 and IPv6 dual stack working on the ASA platform.
Leave a Comment